
Enterprise Platform
Security Across the Platform
MariaDB protects customer data with a robust, end-to-end security strategy that encompasses encryption, access controls, network isolation and secure development practices.
Security you can prove
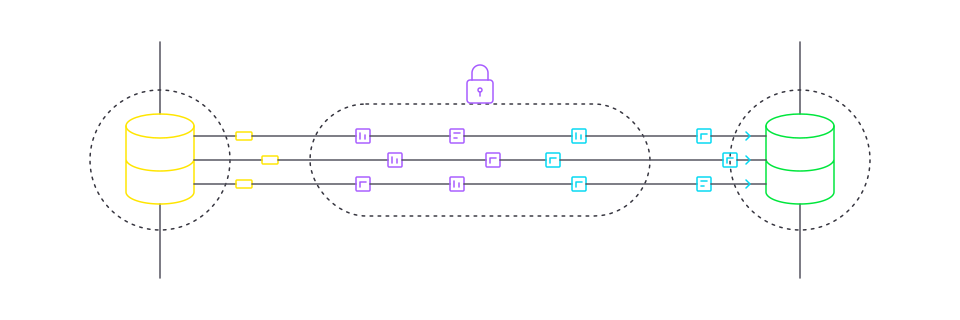
MariaDB Enterprise Platform protects data in transit with TLS and at rest with AES encryption to support PCI-DSS compatibility. It provides granular role-based access control and audit logging. A DoD-approved STIG provides the hardening baseline, and FIPS 140-3 mode runs cryptography on NIST-validated modules.
Benefits
Why MariaDB Enterprise Platform is secure
Hardened to a DoD standard
A DISA-approved Security Technical Implementation Guide gives a published hardening baseline, instead of having to write and defend your own configuration standard.
FIPS 140-3 compliant
Cryptography runs on NIST-validated modules. When deployed with Kubernetes Operator, FIPS 140-3 mode is enabled via a runtime flag.
Encrypted end to end
TLS protects data in transit. AES-based encryption protects data at rest, with keys held in your own key manager.
Controls at every layer
Enterprise Server and MaxScale authenticate each client independently and keep separate audit logs, so data protection doesn’t depend on a single layer.
One trust boundary, anywhere
Bring Your Own Cloud (BYOC) keeps data and compute in your cloud account, providing one security model and trust boundary across on-premises environments and every cloud.
Capabilities
Protection across the platform
Authentication and identity
PAM and LDAP integration, passwordless certificate authentication and support for OpenID Connect SSO (Enterprise Manager, MaxScale and MariaDB GridGain).
Authorization and tenancy
Role-based access control to the object level, plus cache, task, service and system permissions, with multi-tenancy isolation.
Auditing and traceability
The Enterprise Audit plugin logs only chosen events (connections, queries or table access), excludes unneeded objects and assigns different filters per user.
Encryption and key management
AES data-at-rest encryption, SHA-2/PBKDF2-protected key files, passphrase-protected TLS keys, and Vault key management with automatic and manual cache refresh.
Threat and attack protection
The server enforces per-account limits on queries, updates and connections,, while MaxScale filters queries and masks results in front of it.
Secure by design
Security is built into the development lifecycle, with extensive QA before release and security fixes for your release series for long-term stability.
Also supports:
Secure data deserialization
Securing JMX endpoints
Transparent data encryption
Security fixes in your release
Object-level audit filtering
Encrypted DC replication
Key rotation support
Data sovereignty controls
Public CVE disclosure
Query result masking
Per-user resource limits
Looking for Enterprise Platform pricing?
Recommended resources
Get started
Start building with MariaDB
One real-time database platform you can trust, for everything you run today and everything you build next.
Frequently asked questions
Yes. DISA has approved a Security Technical Implementation Guide for MariaDB Enterprise Server, providing a published hardening baseline for accredited deployments rather than requiring you to develop your own configuration standard.
FIPS 140-3 mode runs cryptography on NIST-validated modules. When deploying MariaDB Server with the Kubernetes Operator, it is enabled by a runtime flag, so no separate build or binary is required.
MariaDB maintains an information security management system certified to ISO/IEC 27001:2022 and has achieved SOC 2 Type II. FedRAMP authorization for MariaDB Cloud is targeted for 2027.
Data at rest is encrypted with AES, and the storage engine encrypts before writes and decrypts on reads. Keys are managed in a file-based keystore or an external manager such as HashiCorp Vault.
Yes. MariaDB GridGain supports TLS between nodes, LDAP, passcode and certificate authentication, granular permissions, multi-tenancy isolation, transparent data encryption and full event auditing.
Follow the vulnerability reporting procedure published on mariadb.com. Security fixes are issued for affected release series, allowing you to stay on your release without upgrading to receive patches.